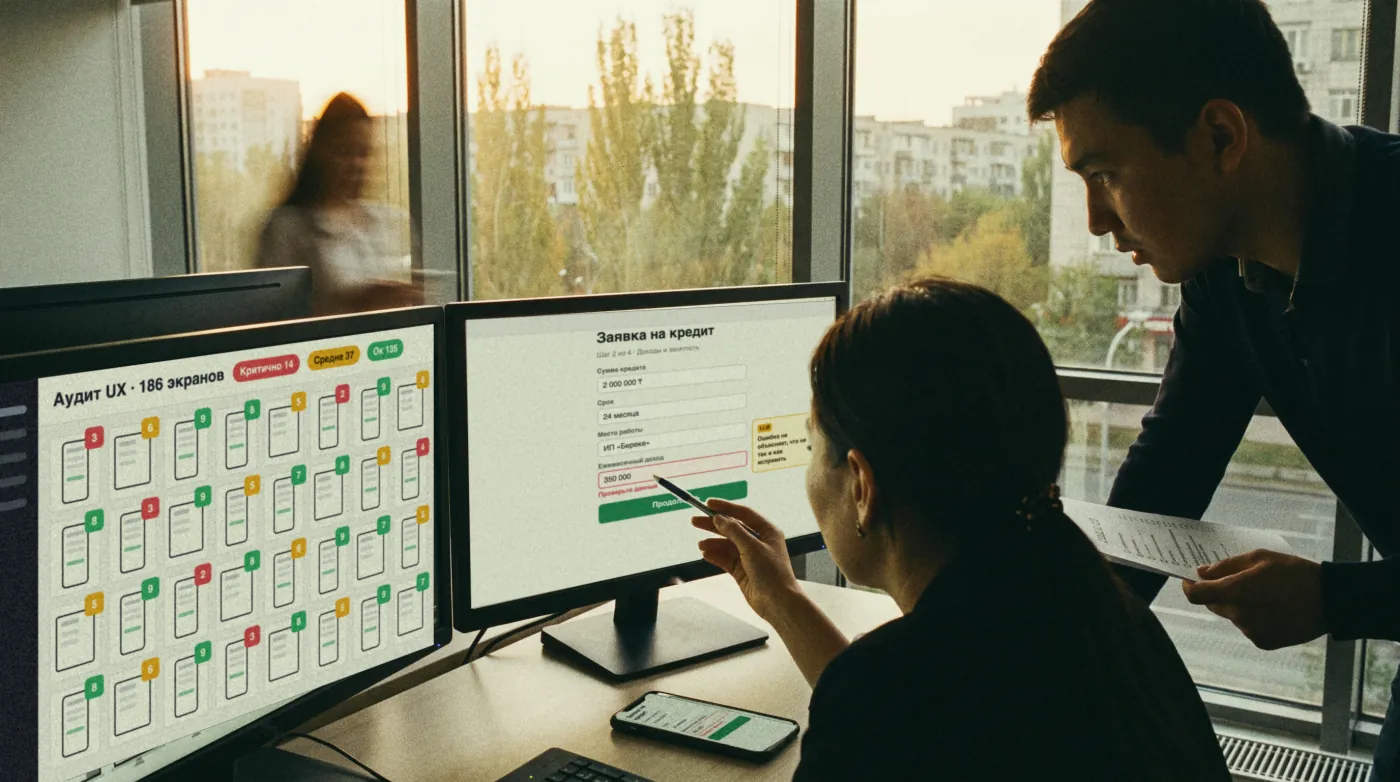
An investor was considering the acquisition of a payment company in Central Asia — a licensed payment institution with a working platform: card issuance, transfers, integrations with card schemes, partner banks and government services.
The seller’s questionnaire answered the question “does the platform work”. The buyer needed something else: how much it would cost to make it resilient and compliant with regulatory requirements — and whether it could support the buyer’s growth plans.
Challenge
- The actual state of the platform — based on code, configuration and documents, not questionnaire answers.
- The cost of getting it in order — which risks to close before the deal, which after, and on what timeline.
- The deal scenario — develop the company as a payment platform or build a digital bank on top of it.
What we assessed
- Application architecture — two linked monoliths and more than 10 services around them.
- Data — 7 databases, message queues, file and secrets storage.
- Infrastructure — cloud, networks and where customer data is physically stored.
- Security — access management, encryption, key management.
- Monitoring — observability, alerting and incident response.
- Integrations — 16 external systems: card schemes, partner banks, government services.
- Backup and recovery — backup retention periods, disaster recovery plan.
How we assessed
The assessment ran in April–May 2026 on the platform’s production configuration.
- 7 cross-checked data sources — the seller’s questionnaire, technology governance documents, source code and infrastructure definitions, data storage schemas, monitoring, antifraud and AML materials, the integration register. Documents and code carry more weight than questionnaire answers.
- Conservative scoring — if a document is mentioned but not provided, the item is marked “pending confirmation” and scored more strictly.
- Maturity — 11 areas, each with three levels: strong, moderate, weak.
- Risks — four levels: critical, high, medium, low. The level depends on how soon the consequences would materialise.
What the assessment showed
Platform maturity is 6.4 out of 10. The strong areas are access management, build and deployment, and environment separation. Eight more are at a moderate level, each with a specific, identified gap. There are no weak areas.
Strengths:
- build, deployment and infrastructure are automated and defined as code, with six strictly isolated environments;
- 16 working integrations — by our estimate, a competitor would need 18–36 months to replicate them;
- a valid PCI DSS compliance report and a working AML/CFT system.
42 risks — 4 critical, 12 high, 21 medium and 5 low. Almost half, 20 of 42, are in security and infrastructure. The critical risks concern cryptographic protection, privileged access control, backup and recovery, and the platform core’s dependence on a single external vendor.
Regulatory requirements. Compliance was checked against five requirements: the critical information infrastructure law, the personal data law, antifraud requirements, PCI DSS v4.0, AML/CFT. The most mature area is AML/CFT. For the rest, gaps are described together with how to fix them.
Two deal scenarios
The same platform fits one scenario and does not fit the other.
- Digital bank — not recommended. The platform has no banking core: no loans, deposits, interest accrual or multi-currency general ledger. It would require a full banking licence and hundreds of new integrations — in effect, building a bank from scratch on top of unresolved risks.
- Payment platform — recommended with conditions. The licence matches the scenario, the platform works and generates revenue, and the technical debt is transparent and can be eliminated within 180 days.
Result
- Recommendation — acquire the company as a standalone payment platform. Stop the valuation models for the digital bank scenario.
- 4 critical risks — to be eliminated before deal closing, with a timeline and plan for each.
- 5 mandatory fixes — secured by a holdback of part of the purchase price or escrow.
- A 180-day post-deal remediation plan — three stages: immediate, short-term and medium-term. All 12 high risks can be eliminated within 90 days by the company itself, without negotiations with counterparties.
- A strategic programme after 180 days — splitting the monoliths into domain services, database clusters, network segmentation.
The investor’s question shifted from “does the platform work” to “how much does it cost to make it resilient and compliant” — and that cost now has clear boundaries.